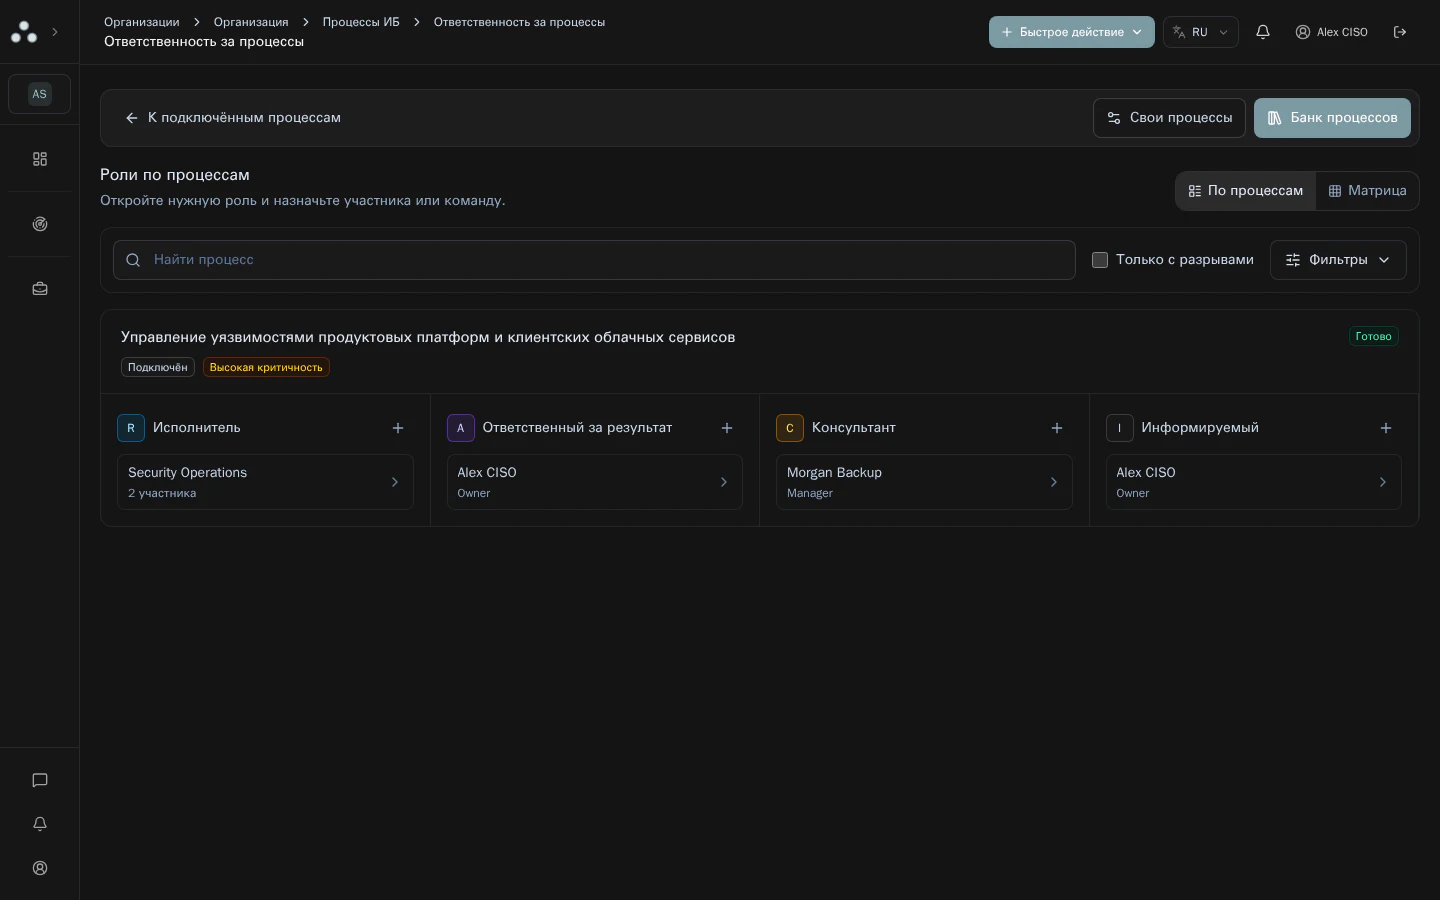
Teams and responsibility
Create your organizational structure and specify who is accountable for results, who does the work, and who only needs to be informed.
An AI platform for continuous information security assurance
Select specific assets and confirm the boundaries before launch. Agents cannot add new targets on their own.
Agents run the required tools themselves. You do not need to gather output from separate consoles and files: actions, errors, and supporting material are kept together in one assessment.
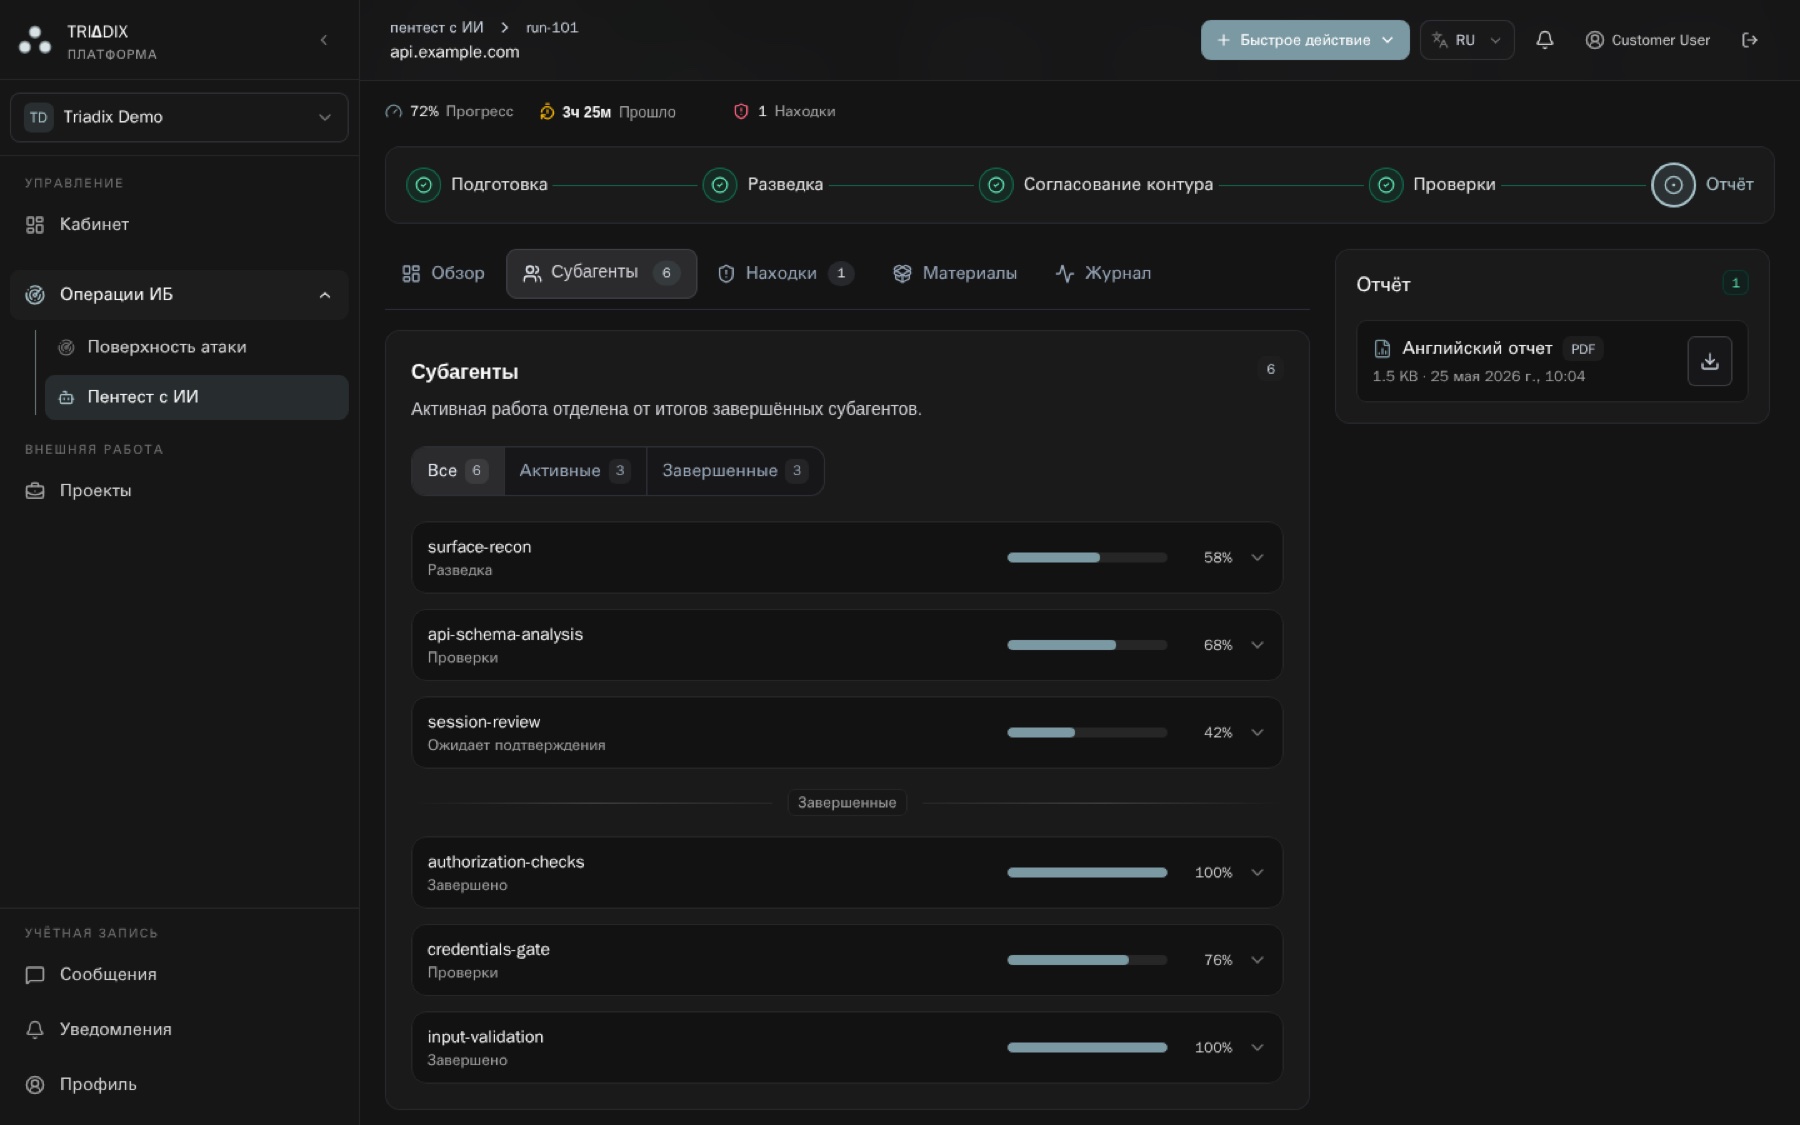
The lead agent splits the run into separate tasks. You can see their status, performed actions, errors, and approval requests.
The final report has the same core contents as a specialist-led pentest: a description of each vulnerability, its impact, reproduction steps, supporting evidence, and remediation guidance.
Specify the authorized domains, hosts, or applications.
Review the settings and explicitly permit execution.
See agent tasks, events, errors, and approvals.
Inspect the description, impact, and supporting material.
Create a task, choose an owner, and schedule a retest.
Create your organizational structure and specify who is accountable for results, who does the work, and who only needs to be informed.
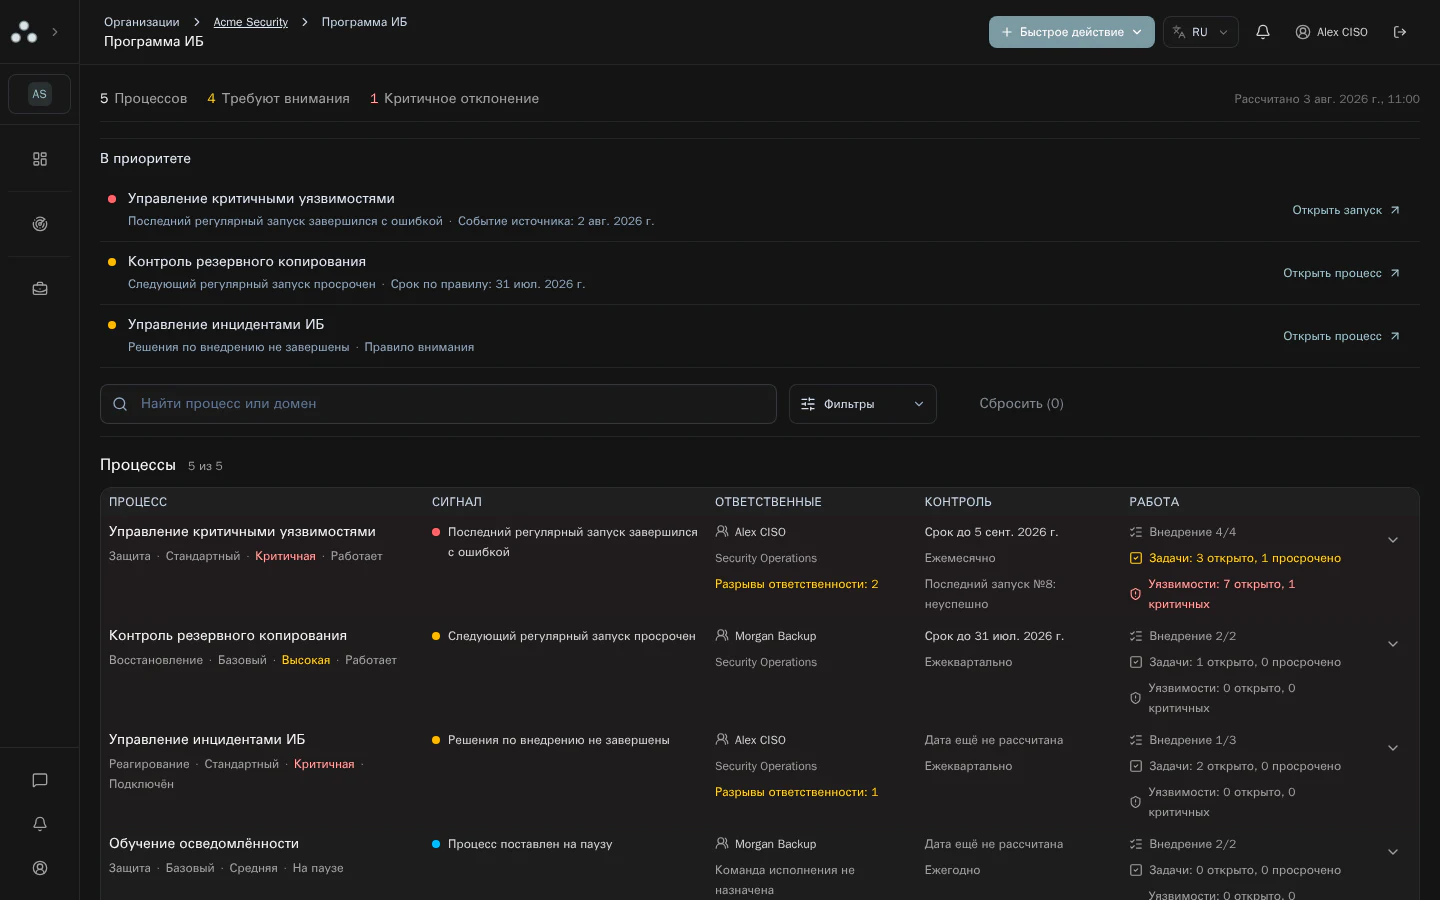
A process is recurring work with an expected result. Define its owner, implementation plan, schedule, and completion criteria.
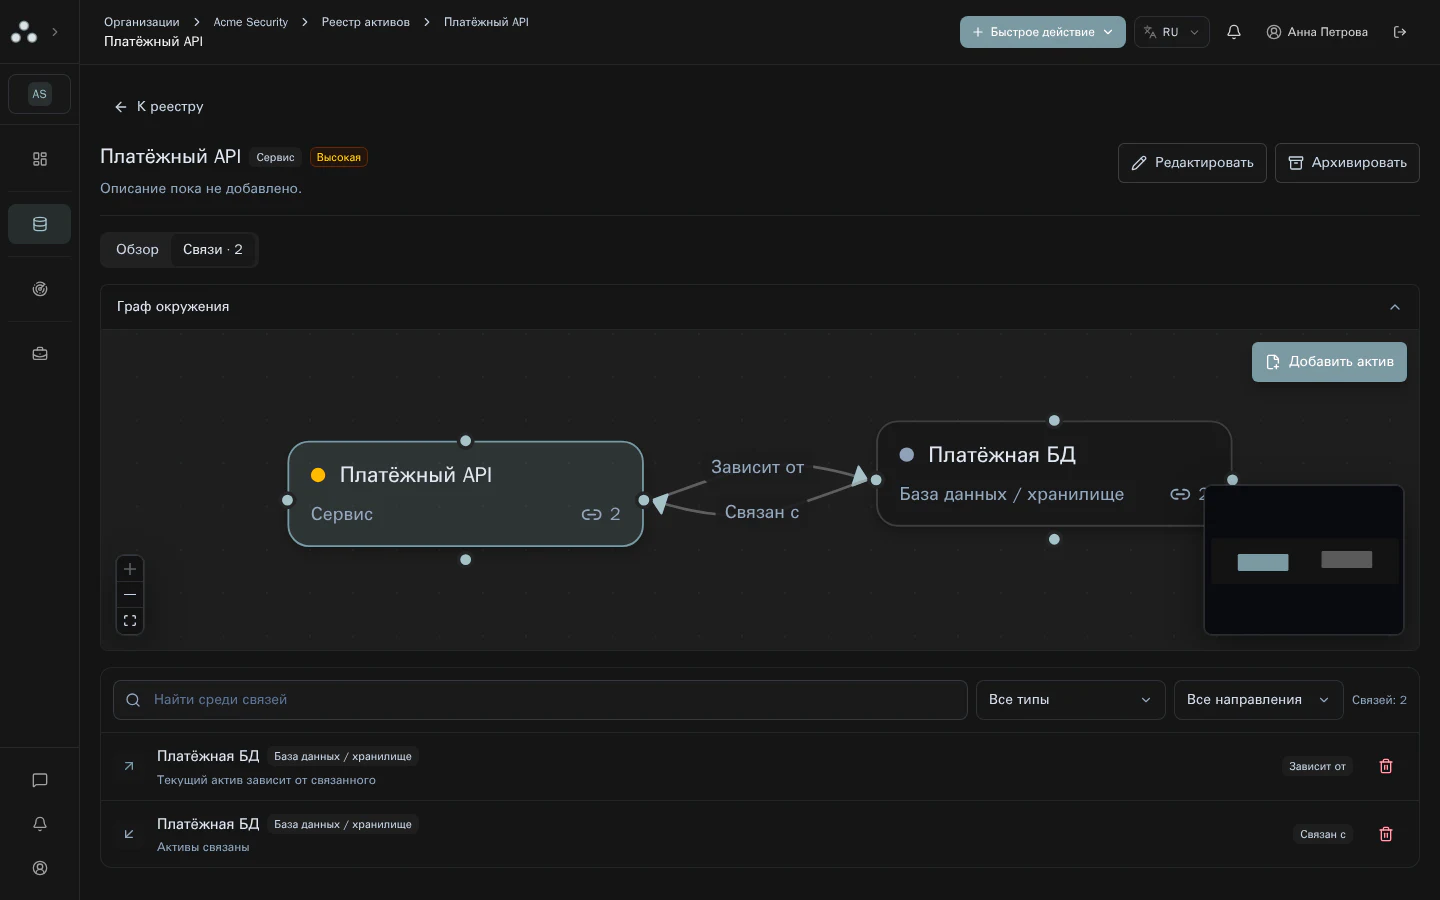
Added assets show which domains, hosts, and applications belong to the organization. Ownership of a domain or host must be verified before it can be scanned.
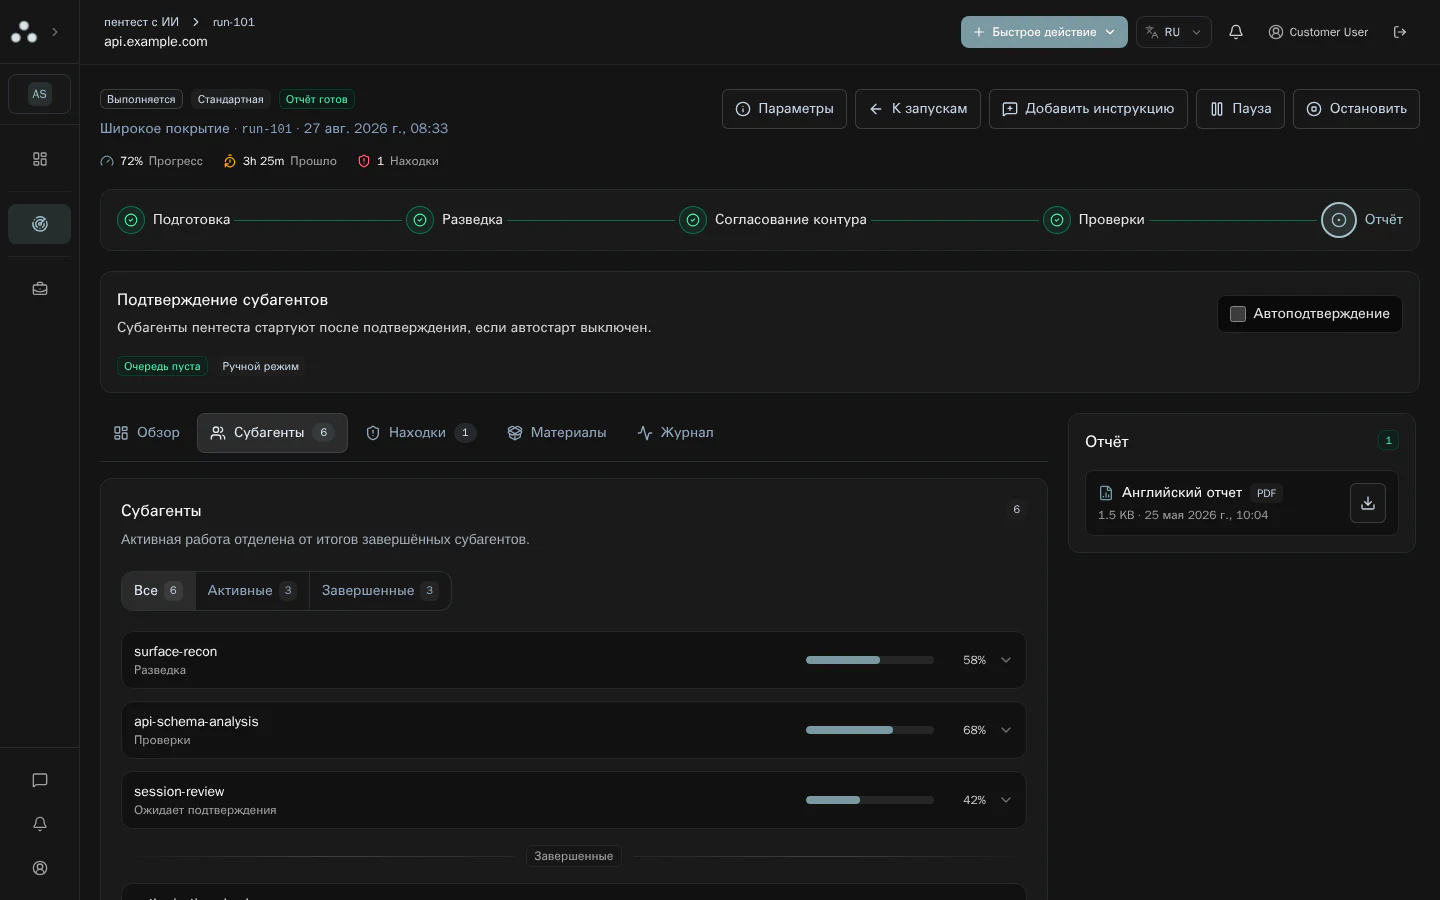
Before launch, select the targets and define how far agents may develop a discovered attack path. During the run, you can see what they are doing and what supports each finding.
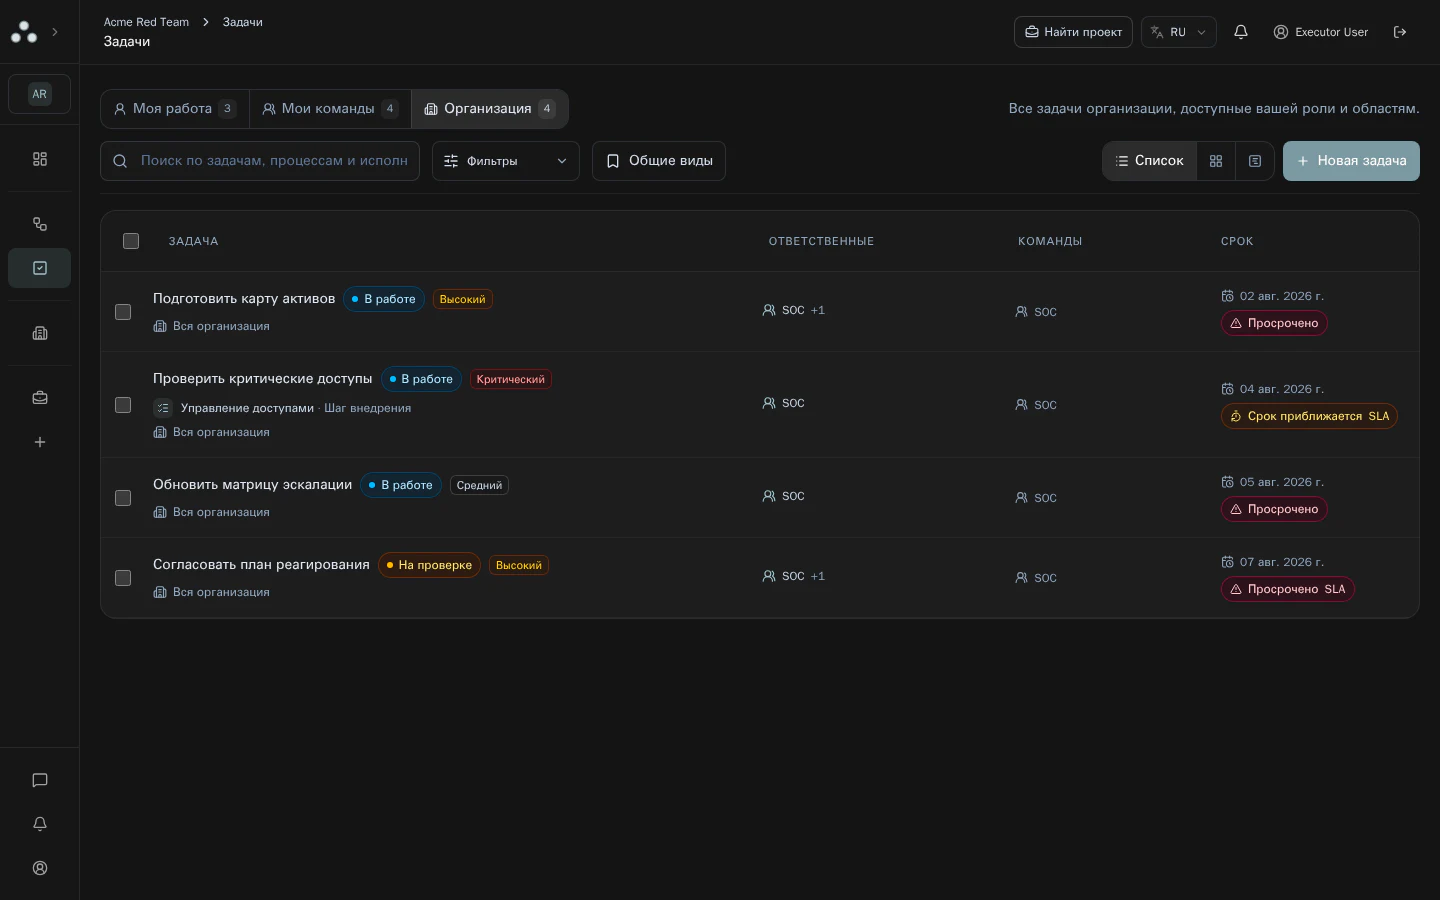
Implementation tasks, discovered vulnerabilities, requirements, and manually created tasks share one list. Every task has a deadline, an owner, and acceptance criteria.
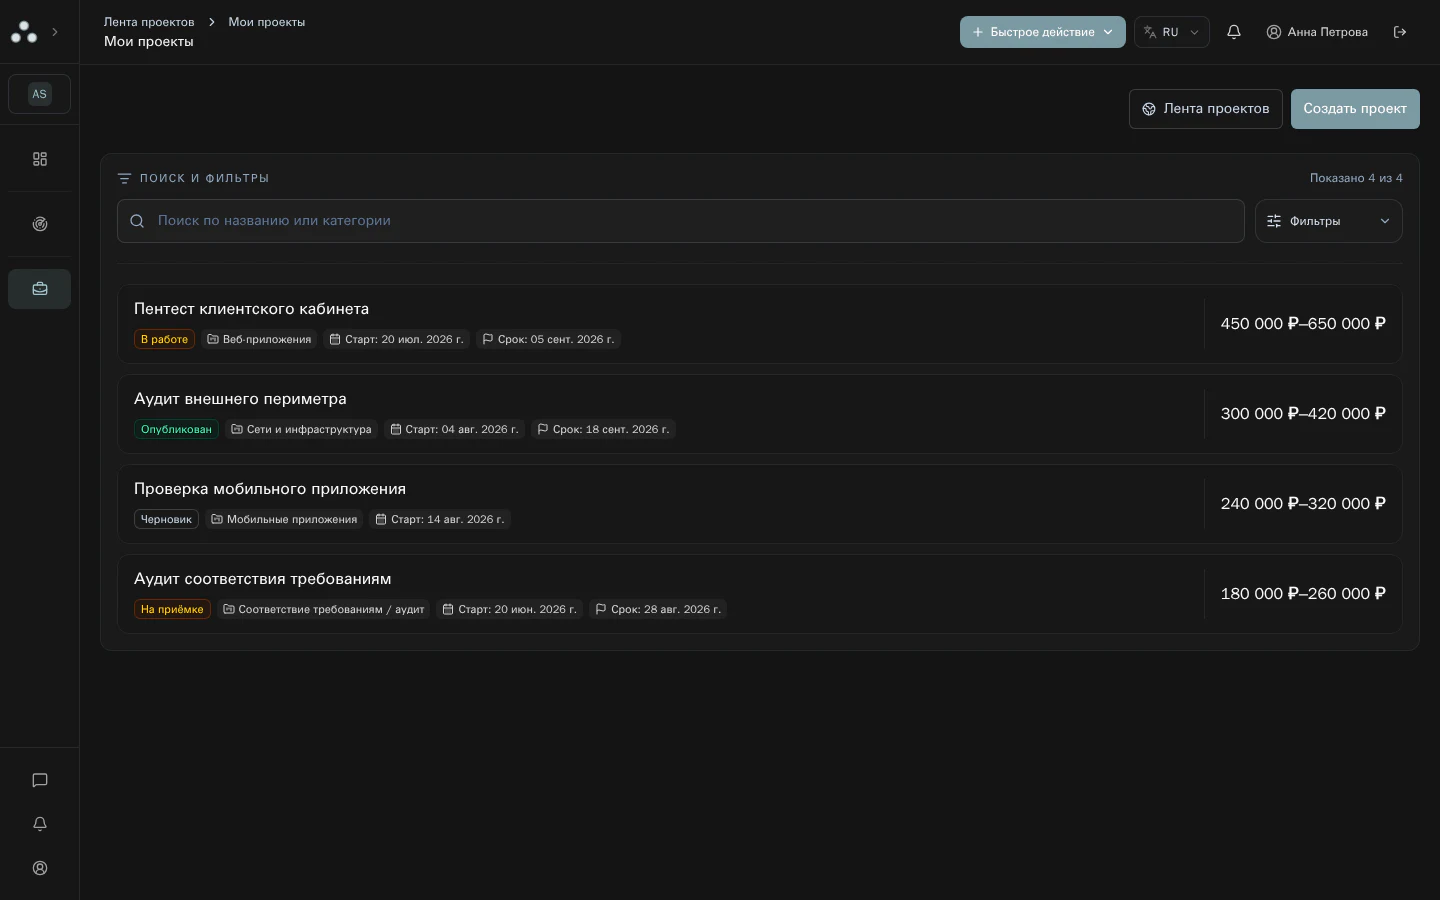
Create a separate assignment for an external specialist. You choose the description and files they can see; they receive no access to other tasks, employees, or internal comments.
The initial assessment is more than a score. It helps you choose work for the coming period, assign owners, and then check whether your defenses have actually improved.
The platform asks about basic security practices: assets, access, vulnerabilities, backups, incidents, and other areas of security work.
Based on your answers, Triadix suggests where to start. Each recommendation shows which answers and rules determined its priority.
Define the process owner, the people doing the work, deadlines, and acceptance criteria. After implementation, the process runs again on a schedule.
After a scan or AI Pentest, a task can be created from a verified vulnerability. It appears in the same list as the rest of the security work.
Attach a report, file, link, or retest result to a completed task. The platform records who accepted the work and when the supporting evidence needs to be updated.
Not every security task needs to be completed by one internal team. In Triadix, work can be assigned to employees, the Triadix team, or a specialist brought in for a specific assignment.
The in-house offensive-security team performs manual assessments and helps investigate complex attack scenarios.
A specific assignment can be given to a professional from the community, such as a pentester, developer, or security-management consultant.
Employees and contractors you already work with complete tasks in the same system.
When handing work to an external specialist, create a separate assignment with a title and description for them, selected files, and acceptance criteria. They cannot see internal comments, organization members, the related process, or other tasks. Once the work is complete, review the result and link it to the original task.
Learn more about the Triadix teamThe SSL-VPN accepts one weak candidate and the external account is compromised.
Without a second factor, the attacker immediately gains external access.
The attacker reaches internal services and begins privilege discovery.
Email, internal services, data, and operational continuity are now at risk.
While you were reading this section, an attacker could already have gained an initial foothold.
 Active in Russia’s information-security community
 Complete confidentiality
 Remediation after attacks
 Certifications and 15 years of experience
AI Pentest reveals weaknesses, the platform provides a specialist to fix them under an NDA, and the CISO calendar and guidelines help you establish the right processes.
Contact me*When you follow recommendations provided during a consultation with TRIADIX specialists
Briefly describe what you need. We’ll find the right specialist on our team and contact you directly.
Attack breakdowns, practical assessments, and changes that materially improve security — in the TRI∆DIX Telegram channel.